America's next fight will reach its networks long before it reaches its shores. Peak protects the defense suppliers, the companies and the local governments an adversary would go after first.
Peak Global brings 3 firms together around one mission: keep American defense data, American businesses and American communities out of an adversary's reach.
The biggest threats to this country no longer arrive by sea or air first. They arrive as a phishing email to a machine shop that builds aircraft parts, a ransomware note on a manufacturer's server, or an intruder inside a county network that runs emergency dispatch.
Each Peak division guards one of those front doors. Peak Complyance gets defense contractors CMMC ready and keeps their designs out of foreign hands. Peak ITSS protects American companies from ransom and intellectual property theft. Peak Gov secures the local governments that public safety, and the military bases beside them, depend on.
The next war will be won or lost long before the first shots are fired, by whose designs are still secret when it starts. We see a defense supply chain that can prove its data is safe, a private sector that keeps the ideas it paid to build, and a public sector that stays online when the country needs it most. Free markets, free trade and a free republic all depend on it.
Every company that touches defense work, and every local government that supports it, sits on the front line. We run protection like the programs our founder has led for 30 years: in order, on paper and with leadership in charge.
Getting compliant changes how the whole company works, so leadership has to own it. Only a third of a CMMC program is technical. The rest is policy, training, roles, accountability and culture, and nearly all 9 types of organizational change come into play. We build programs the executive team runs, with IT as one part of the team.
An assessor and a Department of Justice attorney read the same thing: your documentation. We map every control to dated evidence, so every claim you make can be proven.
State hackers rarely break in through the prime. They come through the 40 person supplier with a shared login, or the county network nobody patched. We start where the attackers start.
Small and mid sized suppliers make much of what the warfighter carries. We keep them eligible for defense work instead of watching compliance costs push them out or force a sale.
Every claim needs a document behind it. We write the evidence, date it and keep it current.
The person pushing the buttons can't be the person grading the work. We sit outside your IT reporting line on purpose.
You get the dated facts and the next step. We don't sell fear, and we don't tell you you're covered when you aren't.
Countywide radio systems, hospital record conversions, CMMC Level 2. We take on the large, regulated projects and deliver them on a real timeline.
You should be able to run the program after we step back. We train your people and hand over a system they can maintain.
Most small defense contractors posted an SPRS score in 2022 and haven't opened the system since. Many of those scores are inflated. One contractor reported a perfect 110, the government scored it at -170, and the company paid $507,144. The False Claims Act reaches recklessness and willful blindness as well as fraud, and you're required to keep the evidence for 6 years, the same window the law gives the government to bring a case.
A failed control can be fixed. A signed score with no documentation behind it is legal exposure. Peak Complyance writes and maintains that documentation for you.

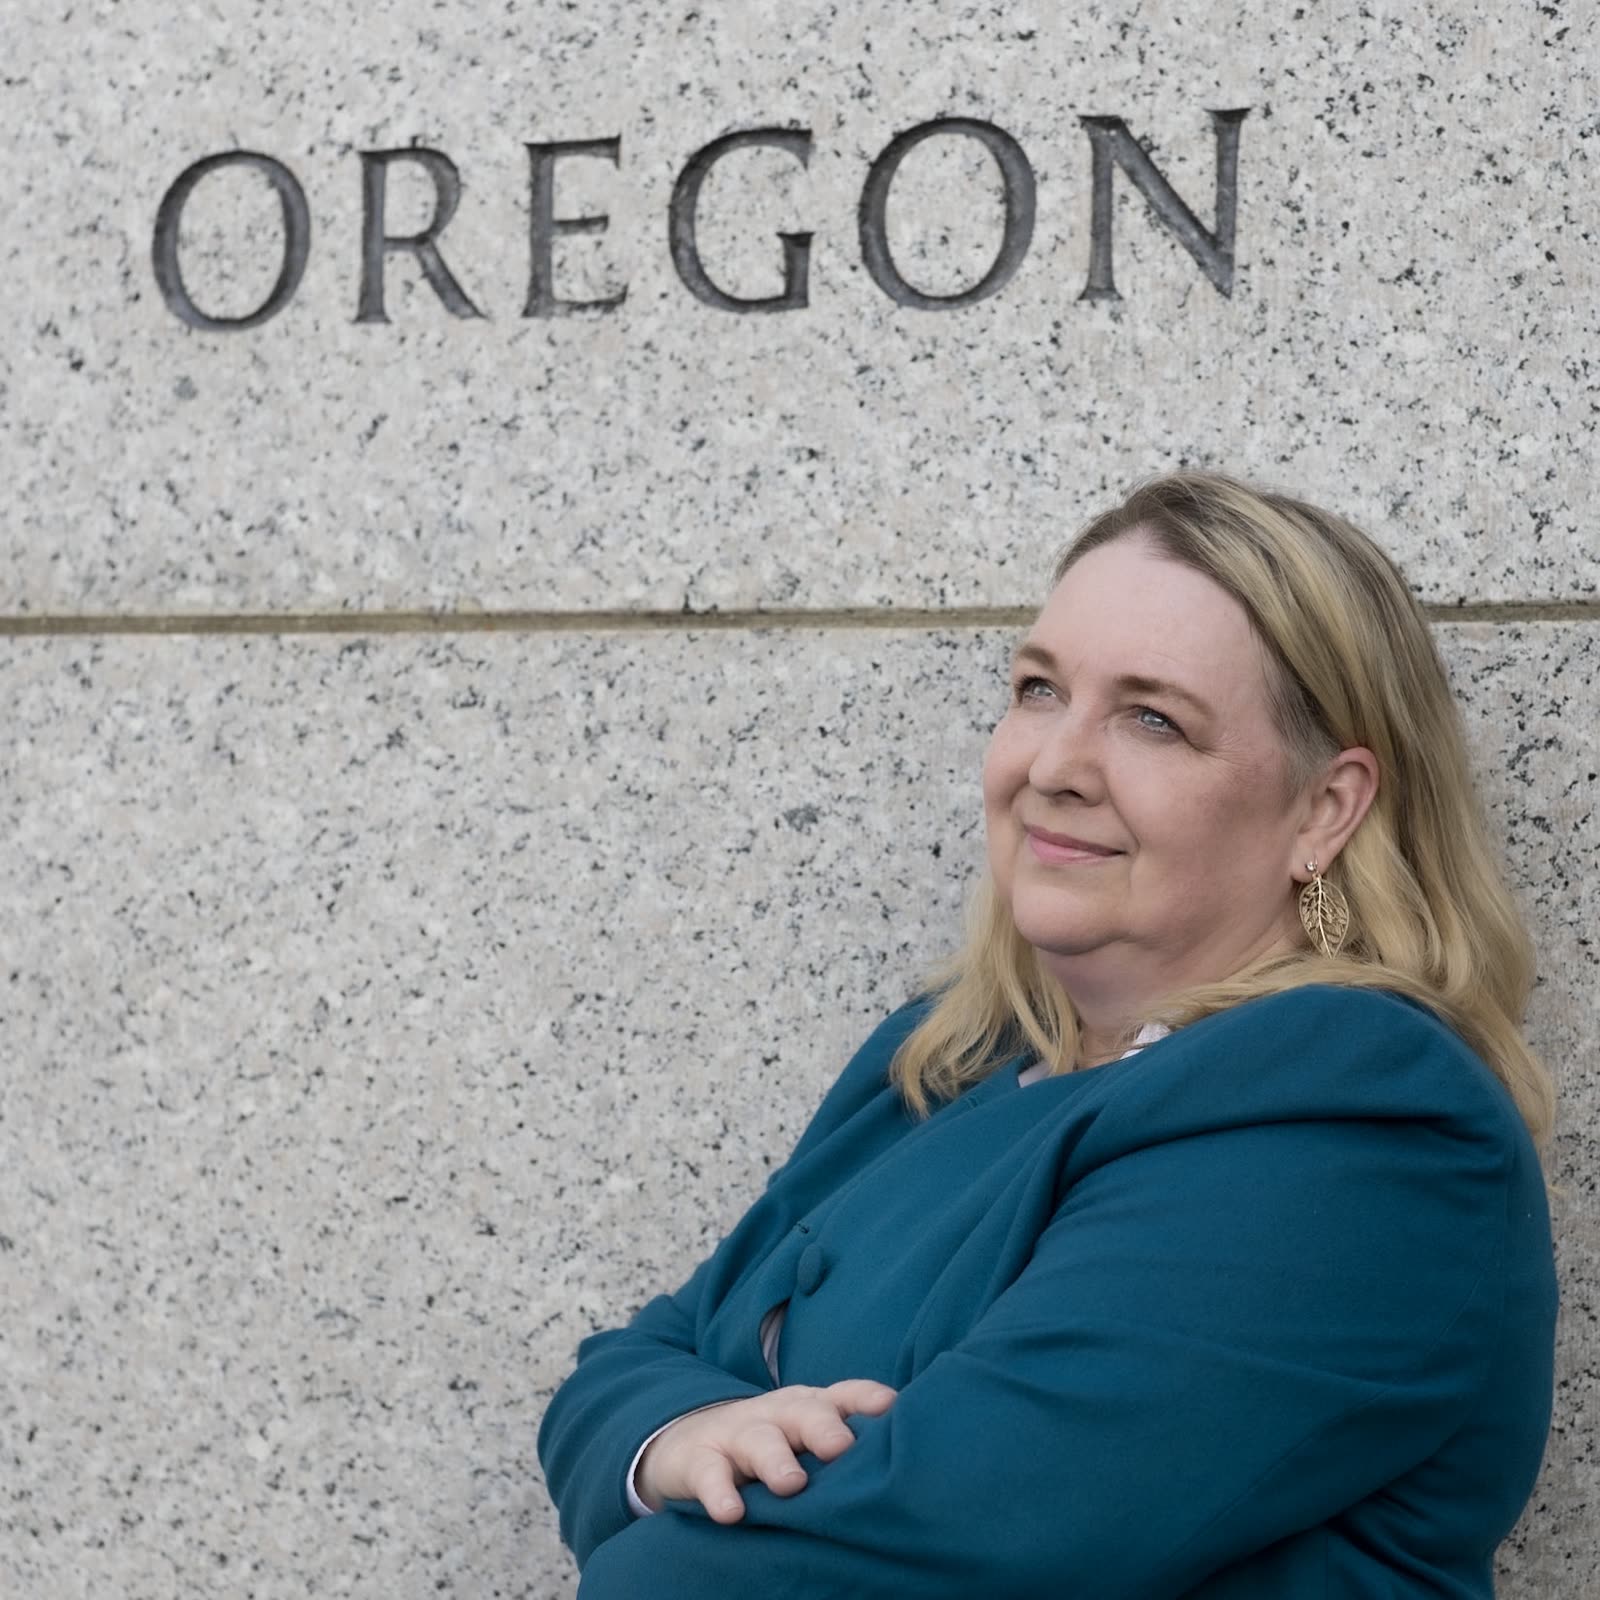
Founder & CEO, Peak Global
Nancy has spent more than 30 years finishing the projects other people called impossible.
She grew up on a ranch in eastern Oregon. For 27 years she was Corporate IT Director for Catholic Health Initiatives, leading IT for 4 hospitals in Oregon, Washington and New Mexico. She built the system's HIPAA security program when HIPAA first took effect and served as its HIPAA Security Officer for 21 years. She moved Mercy Medical Center from paper charts to a fully electronic record and earned nearly $3M in federal incentive payments doing it.
As IT Director for Douglas County, Oregon, she secured more than $20M in federal and state grants, including an $18.25M DHS/FEMA award to rebuild the county's emergency radio system.
Working inside CMMC, NIST 800-171 and DFARS, she watched small defense suppliers get priced out by paperwork. She founded Peak to carry that load for them. She serves on the Advisory Council of the CMMC Implementation Standards Council and the Forbes Coaches Council, and she speaks to defense contractors across the country about what CMMC asks of leadership.
Her central lesson comes from 30 years of large, regulated projects. CMMC is organizational change led from the top, the same kind she ran when hospitals moved to electronic records, and IT runs only one part of it.
"These defense entrepreneurs are the backbone of our country, and they are the ones I'm trying to save, so they are not acquired because the compliance burden is too hard."


Managed IT and cybersecurity for American companies. We lock down the networks, endpoints and backups that stand between your business and a ransom demand, and we keep your designs and client data in your hands.
Enter ITSS →
CMMC and NIST 800-171 compliance for defense contractors. We write and maintain the policies, the SSP and the evidence your assessor reads, so the SPRS score you sign is a true one. Our team includes Certified CMMC Assessors.
Enter Complyance →
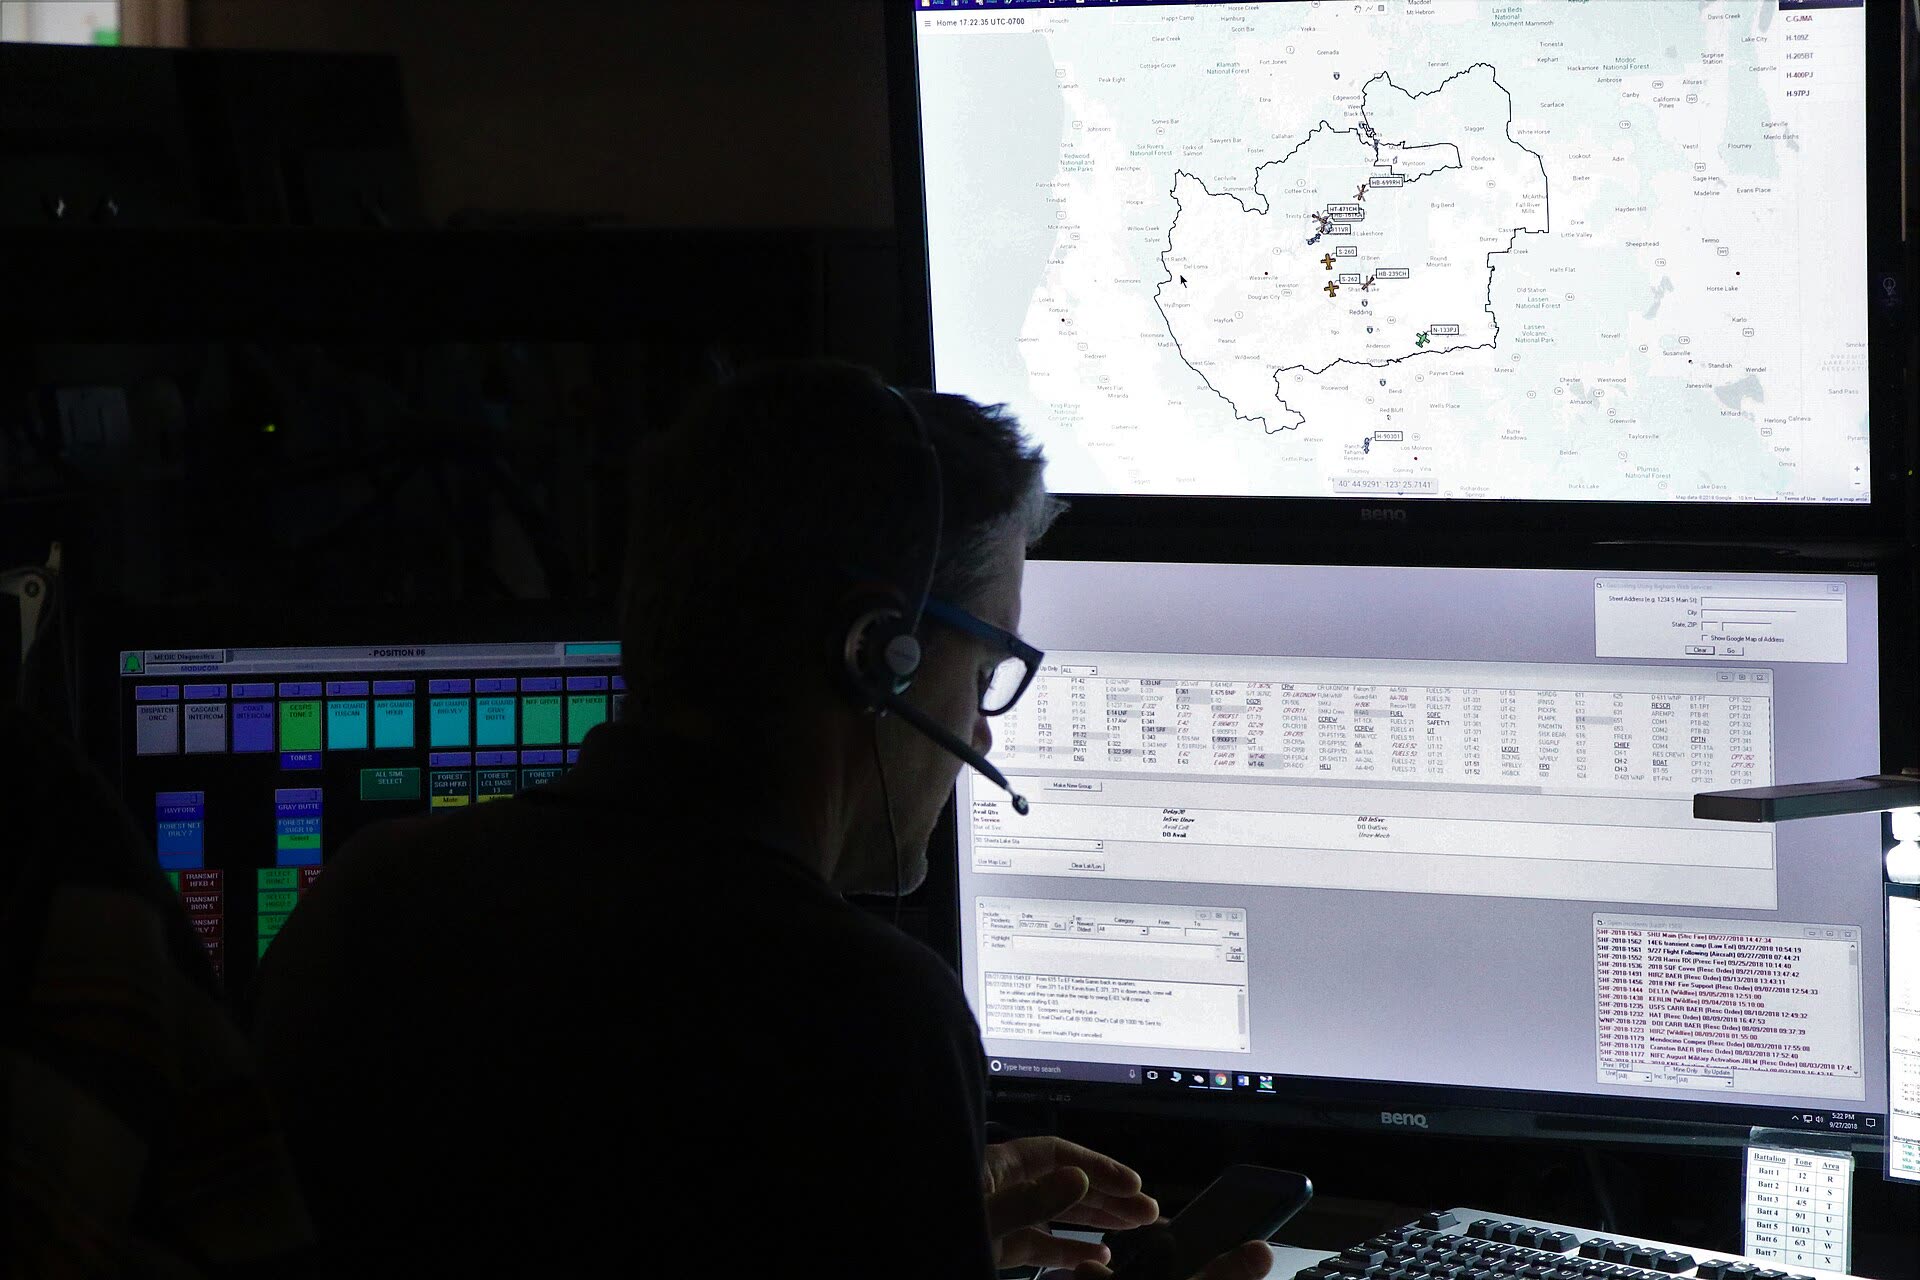
IT, cybersecurity and emergency communications for local government. Counties run the 911 radios, records and networks that residents and nearby military installations depend on. We keep them secure and running.
Enter Gov →For defense contractors, businesses and local governments
Tell us about your organization and the requirements you have to meet. We'll review where you stand and connect you with the right Peak division.
Start a Conversation